"Moving to E5 has been really good from a security point of view... Now we can get a holistic view of what’s going on, which helps us to make changes and recommendations for future plans."
IT Service Manager
Ian Harkess
Trusted by industry leaders
Kickstart Your FastTrack Journey
Fill out the short form below to express your interest in our FastTrack programme, and we’ll be in touch soon.
Please note: A minimum of 150 enterprise licenses is required for FastTrack eligibility.
“We needed to find solutions to a variety of issues whilst being a complex business, operating in a 24/7 environment. Stripe OLT listened and understood immediately the challenges we faced.”
IT Operations Manager
Simon Darley
Trusted by industry leaders
Let's Talk
Call us on one of the numbers below, we cover the whole of the UK, so call the nearest office.
“We needed to find solutions to a variety of issues whilst being a complex business, operating in a 24/7 environment. Stripe OLT listened and understood immediately the challenges we faced.”
This report provides an in‑depth analysis of the Tycoon2FA phishing‑as‑a‑service platform, including how it bypasses MFA and harvests credentials through session authentication cookies. In addition, the report outlines recommended mitigation strategies to help prevent and detect this phishing technique.
“Roses are red, intel is due, the Tycoon is back and is coming for you...”
What is Tycoon2FA phishing?
Tycoon2FA is a phishing-as-a-service (PhaaS) platform first observed in August 2023. It enables large-scale phishing campaigns by providing ready-made tools to cybercriminals.
Developed by the threat actor known as “Storm-1747”, the platform uses adversary-in-the-middle (AiTM) techniques to intercept login sessions and bypass multifactor authentication.
Tycoon2FA has been used in campaigns targeting a wide range of sectors, including education, healthcare, finance, government, and non-profits. At its peak, it supported phishing operations sending tens of millions of messages monthly, impacting over 500,000 organisations worldwide.
This matters because many organisations assume MFA provides sufficient protection against phishing. Platforms like Tycoon2FA are specifically designed to bypass those controls, turning trusted authentication into an attack vector.
How does Tycoon2FA phishing work?
Tycoon2FA campaigns typically begin with phishing emails containing malicious links or attachments. Common lure formats include:
PDF or Word files with QR codes
SVG or HTML attachments with hidden redirect logic
Links disguised as trusted services
These emails use pre-built templates that impersonate services like Microsoft 365, Okta, OneDrive, and DocuSign. Some campaigns also hijack legitimate email threads from compromised accounts to appear more convincing.
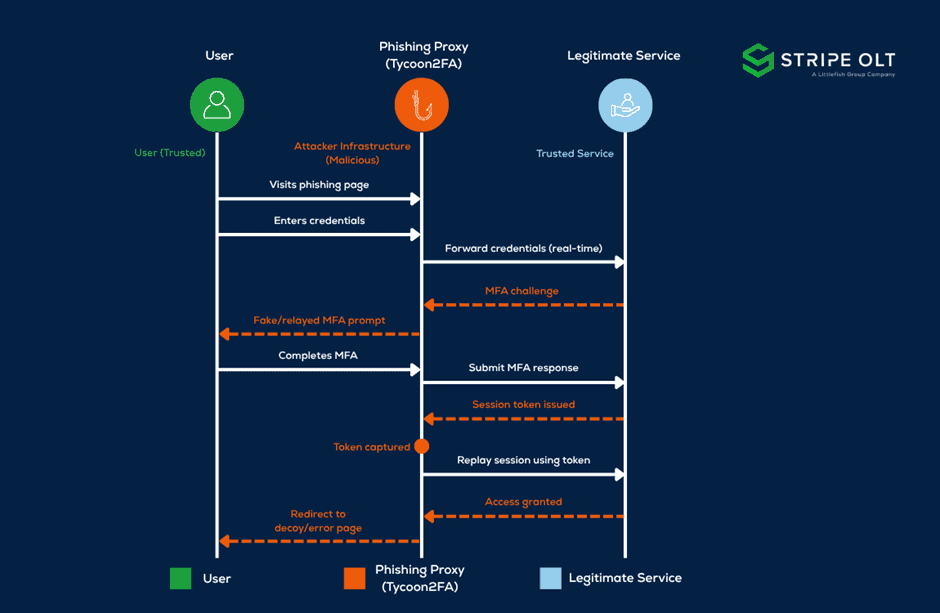
Once a victim interacts with the lure, they are redirected to a fake login page hosted by Tycoon2FA. Using AiTM techniques, the attacker captures login credentials and session tokens, allowing them to bypass MFA and gain account access.
Typical attack flow:
User receives phishing email or QR lure
User is redirected to a fake login page
Attacker proxies the real authentication session
Credentials and session tokens are captured
Attacker gains authenticated access without needing MFA
How Tycoon2FA Takes Over
Caption: A Stripe OLT investigation demonstrating how a fake DocuSign page prompts verification via a real Microsoft login page, compromising the user’s access.
Once a user clicks a phishing link and lands on a masqueraded login page, Tycoon2FA initiates an AiTM attack. Instead of simply stealing credentials, it proxies the real authentication session between the victim and the legitimate service.
In the example above, the victim is presented with:
A fake DocuSign-themed page prompting verification
A real Microsoft login page requesting a device authentication code
The phishing site instructs the user to copy a code from the fake page and enter it into the legitimate Microsoft login window. This is a device code phishing flow, designed to trick the user into authorising access.
Caption: A typical device code phishing flow involving Tycoon2FA.
Real World Incidents
Tycoon2FA has been linked to large-scale global phishing campaigns, impacting organisations across critical sectors.
The healthcare and education sectors were the most affected. Notably, over 100 members of Health-ISAC, a global healthcare threat intelligence group, were successfully compromised.
Mitigation Strategies
In terms of potential mitigation strategies, the following configurations and controls will help prevent an account takeover:
Apply Conditional Access and require secure authentication for privileged and high-risk accounts.
Enforce phishing-resistant strategies. Use passwordless authentication, phishing-resistant MFA methods such as FIDO2 security keys, Windows Hello for Business, and Microsoft Authenticator passkeys.
Turn on Zero-hour auto purge (ZAP) in Defender for Office 365 to quarantine sent mail in response to newly acquired threat intelligence.
Configure automatic attack disruption in Microsoft Defender XDR.
Via Microsoft Defender for Endpoint, enable network protection and cloud-delivered protection to block phishing campaigns.
Enable Safe Links & Safe Attachments – this protects against malicious URLs and files in emails and collaboration tools.
Crucially, educate users to recognise and report phishing emails and associated threats.
A Broader Shift
Tycoon2FA highlights a broader shift in phishing. Attackers are no longer trying to bypass authentication controls directly; they are exploiting how those controls are used in practice.
MFA remains critical, but it is no longer a standalone defence. Session-based attacks, device code phishing, and adversary-in-the-middle techniques are changing what “secure authentication” looks like.
For organisations, the priority is clear. Trust must move beyond credentials and authentication prompts, towards continuous verification, stronger identity controls, and user awareness that reflects how modern phishing actually operates.
Modern Business Email Compromise (BEC) attacks often rely on compromised mailboxes rather than obvious account takeovers. In this article, we'll explore the tactics observed in recent investigations, the signs defenders should look for and practical steps organisations can take to reduce risk.
Remote access technologies have become a staple of modern business operations, enabling secure connectivity for distributed workforces and third-party suppliers. But as cyber defenders have learnt time and time again, threat actors are often quick to adopt the same legitimate tools organisations rely on every day.
Mesh VPN platforms such as Tailscale, Headscale, ZeroTier, Nebula and Netmaker provide secure, encrypted connectivity between devices. While valuable for legitimate remote access, those same capabilities can also be abused by attackers seeking persistent access to compromised systems.
The 2026 Cyber Threat Report explores how attackers are exploiting people, identities and trust to bypass traditional defences, helping UK SME leaders understand the risks they need to prioritise in 2026.
Canary Tokens offer a practical way to strengthen detection and visibility. In this article, we'll explore how they work, where they add value, and how organisations can use them as part of a wider security strategy.
Our SOC team recently uncovered hidden surveillance functionality within a trusted browser extension, including capabilities designed to collect browsing activity, generate unique identifiers and communicate with external infrastructure.
This article breaks down CVE-2026-32201, a zero-day spoofing vulnerability in Microsoft SharePoint Server. You’ll learn how the flaw works, why “spoofing” is more dangerous than it sounds, and what your team needs to do right now if on-premises SharePoint is part of your environment.
This report provides a detailed analysis of OAuth token abuse, focusing on how threat actors bypass defensive security measures to gain unauthorised access.
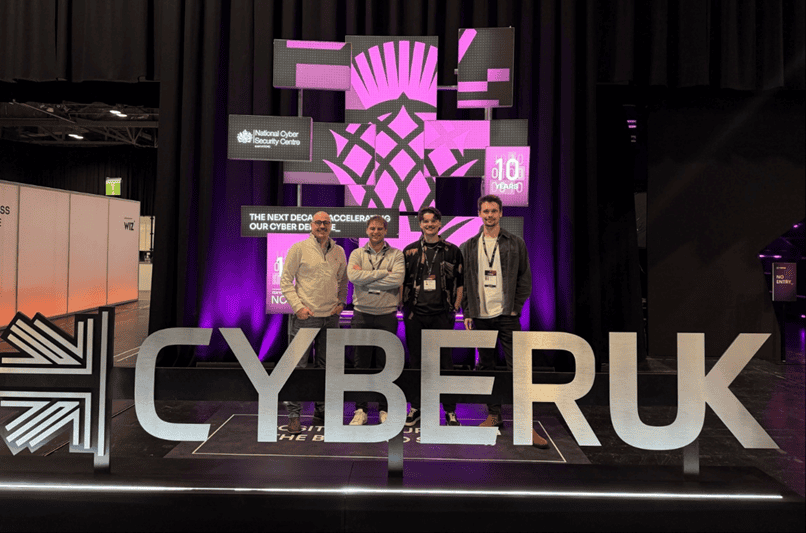
This Expert Intel summarises the key cyber security themes from CYBERUK 2026, exploring how AI is accelerating attacker capability, why identity remains the primary control gap, and what UK based organisations should prioritise to strengthen detection, response, and supply chain resilience.
Microsoft is reshaping its licensing strategy with the introduction of Microsoft 365 E7, new pricing changes, continued Teams separation, and additional security and AI functionality being bundled into existing licences. For organisations investing in AI, automation, security, and compliance, these changes could significantly affect licensing costs, procurement decisions, and long-term Microsoft 365 strategy.
This report provides an in‑depth analysis of the Tycoon2FA phishing‑as‑a‑service platform, including how it bypasses MFA and harvests credentials through session authentication cookies. In addition, the report outlines recommended mitigation strategies to help prevent and detect this phishing technique.
In this intel we set out to understand the changing landscape of trust, in a digital world where AI-generated code is permeating the software supply chain at scale and AI-enabled phishing is making adversarial infrastructure harder than ever to distinguish from the real thing.
This website uses cookies. By using this site you agree to our use of cookies. We use cookies to enhance your experience. To understand the specific cookies we use and how we handle your data, see our Cookie Policy, Privacy Policy and Terms & Conditions. Manage your preferences at any time by clicking the 'View Preferences' button.
Functional
Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes.The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.