"Moving to E5 has been really good from a security point of view... Now we can get a holistic view of what’s going on, which helps us to make changes and recommendations for future plans."
IT Service Manager
Ian Harkess
Trusted by industry leaders
Kickstart Your FastTrack Journey
Fill out the short form below to express your interest in our FastTrack programme, and we’ll be in touch soon.
Please note: A minimum of 150 enterprise licenses is required for FastTrack eligibility.
“We needed to find solutions to a variety of issues whilst being a complex business, operating in a 24/7 environment. Stripe OLT listened and understood immediately the challenges we faced.”
IT Operations Manager
Simon Darley
Trusted by industry leaders
Let's Talk
Call us on one of the numbers below, we cover the whole of the UK, so call the nearest office.
“We needed to find solutions to a variety of issues whilst being a complex business, operating in a 24/7 environment. Stripe OLT listened and understood immediately the challenges we faced.”
This report provides a detailed analysis of OAuth token abuse, focusing on how threat actors bypass defensive security measures to gain unauthorised access.
“Security is gold, but tokens are bold, your session is sold before it gets old.”
As organisations continue to accelerate cloud adoption and embrace SaaS-driven ecosystems, identity and access management has become one of the most critical pillars of modern cyber security. However, while businesses invest heavily in strengthening authentication controls such as Multi-Factor Authentication (MFA), attackers are increasingly shifting tactics to exploit the trust mechanisms that exist beyond passwords – this is where OAuth token abuse comes in…
So, what exactly is OAuth token abuse?
OAuth allows third-party applications access to cloud app resources such as Outlook files without the requirement of a password, using tokens as an authorisation method. OAuth token abuse occurs when threat actors bypass credentials entirely, either by stealing a valid session token or tricking a user into granting permission to a malicious “shadow” application. This matters because OAuth removes the need for passwords, but in doing so shifts trust to tokens and application permissions. When abused, this allows attackers to bypass traditional controls such as MFA and conditional access entirely.
While OAuth was designed to improve usability and streamline secure access between applications, the same convenience can create opportunities for abuse when permissions are granted too broadly or monitored too loosely. Because many of these actions appear legitimate from the perspective of the identity provider, traditional detection methods may struggle to identify malicious behaviour early.
How does it work?
OAuth token abuse typically falls into three attack paths:
Token Theft – When a threat actor steals an OAuth token used to access APIs and other services, without the requirement to re-authenticate.
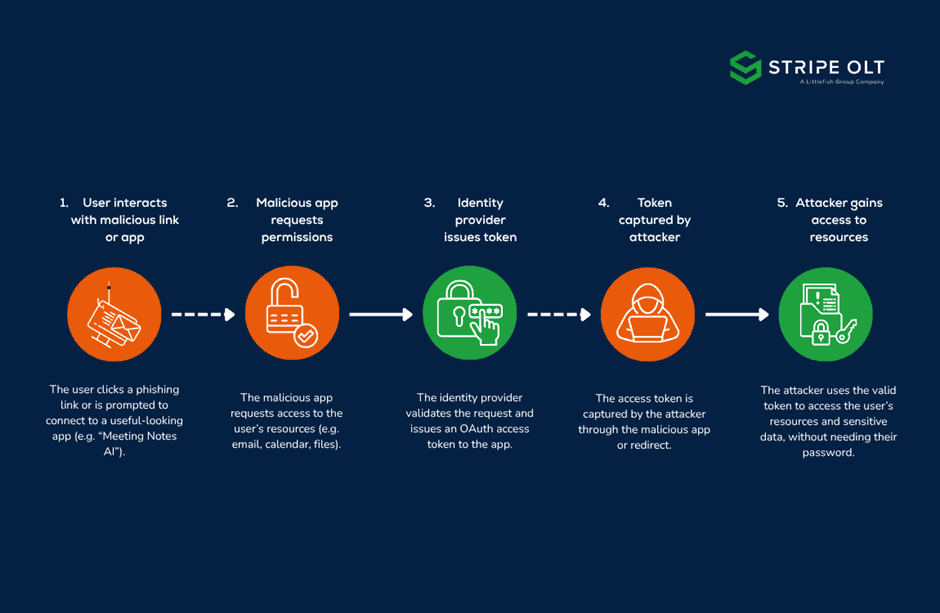
Session Hijacking – This involves taking over an active session or tricking a user into authorising a malicious app. Attackers create fake apps (e.g. “Meeting Notes AI”) with legitimate-looking consent screens. When a user clicks “Accept”, the identity provider issues a valid token directly to the attacker.
Device Code Phishing – Attackers use the “Device Flow” to trick users into authorising an attacker’s device. This is particularly dangerous because it often bypasses conditional access policies that require “Managed Devices”.
Caption:Example attack flow showing how malicious OAuth apps mimic legitimate services, making it difficult for users to distinguish safe from unsafe permissions.
The effectiveness of these techniques lies in the fact that attackers are abusing trusted processes rather than exploiting software vulnerabilities directly. In many cases, organisations may unknowingly approve malicious applications or overlook dormant third-party integrations that retain excessive permissions long after implementation.
Real World Incidents
Real-world breaches over the past year demonstrate how OAuth token abuse is no longer a theoretical risk, but an increasingly active attack vector affecting major organisations and SaaS providers globally. Two notable breaches include:
As reported by Trend Micro, OAuth token abuse contributed to the Vercel Breach. A compromised third-party OAuth app (Context.ai) allowed attackers to pivot into Vercel’s internal systems and bypass traditional security controls. This demonstrated how a single “non-human” trust relationship can expose sensitive data.
Mitigation strategies against OAuth token abuse
Reducing the risk of OAuth token abuse requires organisations to rethink how application trust and delegated access are governed across their environments. Security teams should focus not only on user authentication, but also on continuous visibility and control over application permissions.
Restrict Third-Party Apps – Disable the ability for users to grant permissions to unverified applications. Implement a secure and protected workflow for all new OAuth integrations.
Shorten Token Lifespans – Use refresh token rotation and enforce shorter expiration times to reduce the window of opportunity for a stolen token.
Continuous Inventory – Regularly audit all SaaS-to-SaaS integrations and “shadow AI” tools to ensure no legacy apps still have high-privilege access to your data.
Enforce Phishing-Resistant MFA – Shift to FIDO2/WebAuthN or hardware security keys. Unlike traditional “push” notifications, these methods use cryptographic signatures that cannot be intercepted or replayed by attackers.
OAuth token abuse highlights a broader shift in identity-based attacks – where trust is no longer tied to credentials, but to permissions that are often less visible and less controlled.
If you would like to understand how OAuth token abuse could impact your environment or review your current identity controls, you can speak to our team.
Modern Business Email Compromise (BEC) attacks often rely on compromised mailboxes rather than obvious account takeovers. In this article, we'll explore the tactics observed in recent investigations, the signs defenders should look for and practical steps organisations can take to reduce risk.
Remote access technologies have become a staple of modern business operations, enabling secure connectivity for distributed workforces and third-party suppliers. But as cyber defenders have learnt time and time again, threat actors are often quick to adopt the same legitimate tools organisations rely on every day.
Mesh VPN platforms such as Tailscale, Headscale, ZeroTier, Nebula and Netmaker provide secure, encrypted connectivity between devices. While valuable for legitimate remote access, those same capabilities can also be abused by attackers seeking persistent access to compromised systems.
The 2026 Cyber Threat Report explores how attackers are exploiting people, identities and trust to bypass traditional defences, helping UK SME leaders understand the risks they need to prioritise in 2026.
Canary Tokens offer a practical way to strengthen detection and visibility. In this article, we'll explore how they work, where they add value, and how organisations can use them as part of a wider security strategy.
Our SOC team recently uncovered hidden surveillance functionality within a trusted browser extension, including capabilities designed to collect browsing activity, generate unique identifiers and communicate with external infrastructure.
This article breaks down CVE-2026-32201, a zero-day spoofing vulnerability in Microsoft SharePoint Server. You’ll learn how the flaw works, why “spoofing” is more dangerous than it sounds, and what your team needs to do right now if on-premises SharePoint is part of your environment.
This report provides a detailed analysis of OAuth token abuse, focusing on how threat actors bypass defensive security measures to gain unauthorised access.
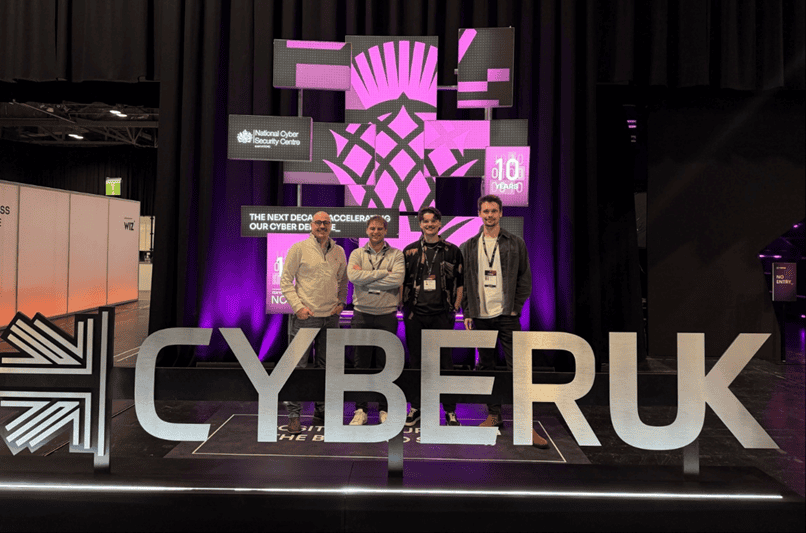
This Expert Intel summarises the key cyber security themes from CYBERUK 2026, exploring how AI is accelerating attacker capability, why identity remains the primary control gap, and what UK based organisations should prioritise to strengthen detection, response, and supply chain resilience.
Microsoft is reshaping its licensing strategy with the introduction of Microsoft 365 E7, new pricing changes, continued Teams separation, and additional security and AI functionality being bundled into existing licences. For organisations investing in AI, automation, security, and compliance, these changes could significantly affect licensing costs, procurement decisions, and long-term Microsoft 365 strategy.
This report provides an in‑depth analysis of the Tycoon2FA phishing‑as‑a‑service platform, including how it bypasses MFA and harvests credentials through session authentication cookies. In addition, the report outlines recommended mitigation strategies to help prevent and detect this phishing technique.
In this intel we set out to understand the changing landscape of trust, in a digital world where AI-generated code is permeating the software supply chain at scale and AI-enabled phishing is making adversarial infrastructure harder than ever to distinguish from the real thing.
This website uses cookies. By using this site you agree to our use of cookies. We use cookies to enhance your experience. To understand the specific cookies we use and how we handle your data, see our Cookie Policy, Privacy Policy and Terms & Conditions. Manage your preferences at any time by clicking the 'View Preferences' button.
Functional
Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes.The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.