"Moving to E5 has been really good from a security point of view... Now we can get a holistic view of what’s going on, which helps us to make changes and recommendations for future plans."
IT Service Manager
Ian Harkess
Trusted by industry leaders
Kickstart Your FastTrack Journey
Fill out the short form below to express your interest in our FastTrack programme, and we’ll be in touch soon.
Please note: A minimum of 150 enterprise licenses is required for FastTrack eligibility.
“We needed to find solutions to a variety of issues whilst being a complex business, operating in a 24/7 environment. Stripe OLT listened and understood immediately the challenges we faced.”
IT Operations Manager
Simon Darley
Trusted by industry leaders
Let's Talk
Call us on one of the numbers below, we cover the whole of the UK, so call the nearest office.
“We needed to find solutions to a variety of issues whilst being a complex business, operating in a 24/7 environment. Stripe OLT listened and understood immediately the challenges we faced.”
PHP to Prevention: The Importance of Cyber Security Fundamentals
Published: October 30, 2026
In a nutshell:
Recent PHP vulnerabilities have highlighted how quickly new cyber risks can emerge. While most business leaders won't need to understand the technical details themselves, it's important that the teams and providers responsible for your technology do. The story serves as a timely reminder that strong cyber hygiene remains one of the most effective ways to reduce cyber risk.
"The technologies making the headlines may change, but the fundamentals of cyber security remain the same."
If you’ve followed the news recently, you’ve probably seen reports about newly discovered PHP vulnerabilities. The warning prompted action from governments, website operators and technology providers around the world, with some organisations temporarily taking websites offline while updates were applied.
For many business leaders, the immediate reaction was probably: What is PHP, and does this affect me?
The good news is that most organisations won’t need to understand the technical details or patch affected systems themselves. That’s the job of website providers, software vendors and IT teams. However, the recent PHP story does provide a useful reminder of a broader lesson: cyber threats are constant, whether you understand the impact of them or not – strong cyber hygiene remains one of the most effective ways to reduce risk.
First Things First: What Is PHP?
PHP is a programming language used to power websites, web applications and online services. It works behind the scenes, helping websites display content, process forms, connect to databases and deliver the functionality users expect.
While many people have never heard of PHP, it’s one of the most widely used technologies on the internet. PHP is used by around 69% of websites where the server-side programming language can be identified.
That means a vulnerability affecting PHP has the potential to impact a huge number of organisations, products and services. Importantly, many businesses may not even realise PHP is being used behind the scenes, as it is often embedded within websites, applications and platforms managed by third parties.
Why Has PHP Been in the News?
In October 2026, the National Cyber Security Centre (NCSC) warned organisations about two critical vulnerabilities affecting PHP. These vulnerabilities could allow attackers to remotely execute malicious code on vulnerable servers if left unpatched.
The issue attracted significant attention because of PHP’s widespread use and the potential impact on internet-facing systems. Security agencies and cyber authorities across the UK, Europe and beyond urged organisations to prioritise updates and remediation activities.
For the average business, however, the most important takeaway isn’t the technical vulnerability itself.
It’s what the story tells us about cyber security in general.
The Unknown Is Always Out There
New vulnerabilities are discovered all the time. Some attract widespread attention, while many others pass largely unnoticed.
The challenge for organisations is that they can’t predict which technology will appear in tomorrow’s headlines. That’s why cyber resilience isn’t built on reacting to individual vulnerabilities, but on maintaining strong foundations.
Whether it’s PHP today or another piece of software tomorrow, organisations with good cyber hygiene are far better positioned to respond quickly and effectively.
What Good Cyber Hygiene Looks Like
When people hear the term “cyber security”, they often think of advanced tools, complex technologies and sophisticated attacks.
In reality, many of the most important security measures are surprisingly straightforward.
Keep Systems Up to Date
The PHP story is a perfect example of why patching matters.
When software vendors release security updates, they are often addressing newly discovered vulnerabilities. Applying those updates in a timely manner helps reduce the window of opportunity for attackers.
Most businesses won’t be responsible for patching PHP directly, but they should have confidence that their website partner or internal technology team has robust patch management processes in place.
Know Who Looks After What
Modern businesses rely on a wide range of suppliers, platforms and service providers. A company website may be managed by an external web agency, cloud services may be maintained by a technology partner, and cyber security monitoring may sit with a specialist provider.
While organisations retain responsibility for managing cyber risk, many day-to-day security activities are carried out by trusted third parties. Understanding who owns each part of your environment, and where responsibilities begin and end, helps ensure important updates, patches and security actions don’t fall through the cracks.
Caption: Understanding the areas your organisation directly controls, and the systems and services managed by third parties, is an important part of maintaining good cyber hygiene. Source: Stripe OLT – 2026 Cyber Threat Report
Stay Informed
Business leaders don’t need to become cyber security experts, but they do need to understand the risks that matter to their organisation and help their teams respond.
Vulnerabilities like the recent PHP flaw are a reminder that cyber security requires ongoing attention. Staying informed, asking the right questions and working closely with internal teams, technology providers and security professionals all help turn awareness into action.
Build Security Into Everyday Operations
Good cyber hygiene isn’t just about technology. It also means creating business processes that support security, this could look like:
Strengthening identity and access controls, enforcing least privilege, limiting administrator access and using conditional access policies to restrict sign-ins based on device security, location and risk.
Maintaining an accurate asset inventory, including internet-facing applications and underlying software components, so affected systems can be identified quickly when vulnerabilities emerge.
Continuously managing vulnerabilities, using regular scanning and prioritising fixes based on active exploitation, exposure and business impact.
Verifying that patches work, checking that updates have been applied successfully and the vulnerability has been resolved.
Hardening systems and segmenting networks, removing unnecessary services and restricting connections to reduce opportunities for attackers to move between systems.
Centralising security logs and monitoring, with clear responsibility for investigating suspicious activity and responding to potential compromise.
The Bigger Lesson for SMEs
The recent PHP vulnerabilities are a useful reminder that cyber threats continue to evolve and that new risks can emerge with little warning.
While organisations can’t predict every vulnerability that will emerge, they can build the habits, processes and foundations that help them respond with confidence when the next headline arrives. The threats making the news may change, but the value of good cyber hygiene remains constant.
Staying on Top of Cyber Risk
Strong cyber security starts with strong foundations. Whether you’re looking to improve cyber hygiene, strengthen vulnerability management or enhance resilience, the right expertise can help you stay ahead of evolving risks.
If you’d like to discuss how your organisation can strengthen its cyber security foundations,speak to our team of experts.
Want to learn more about the cyber risks and trends shaping today’s threat landscape? Our 2026 Cyber Threat Report looks at the real-world threats facing organisations today and highlights the practical controls that can help reduce cyber risk. Download your copy.
Recent PHP vulnerabilities show how security risks can emerge in technologies organisations may not even know they use. This article explores why cyber hygiene matters beyond any single flaw, and how timely patching, clear supplier responsibilities, asset visibility and ongoing monitoring help reduce risk.
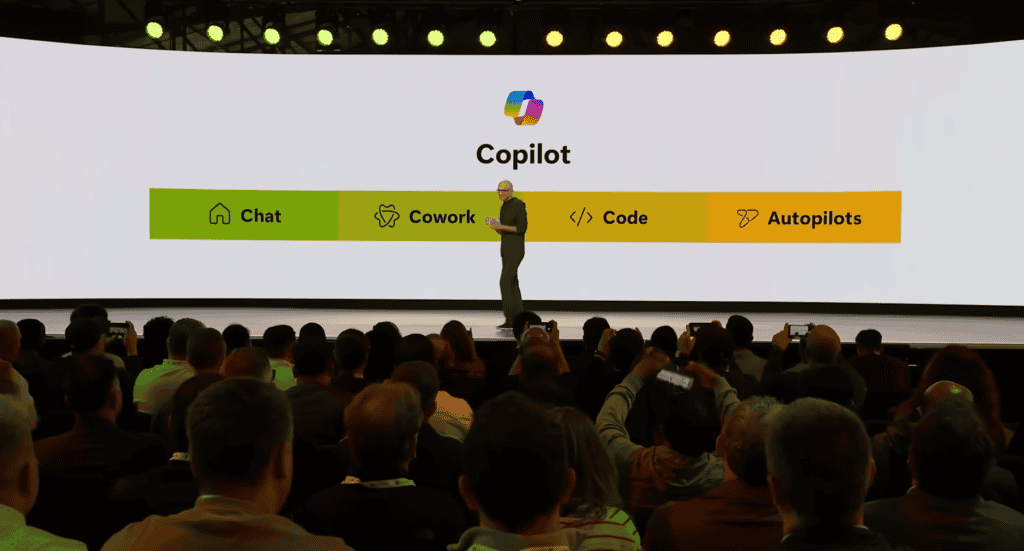
From AI agents to enhanced Copilot capabilities, June’s Microsoft Build highlighted how organisations can move from AI experimentation to practical, business-focused adoption.
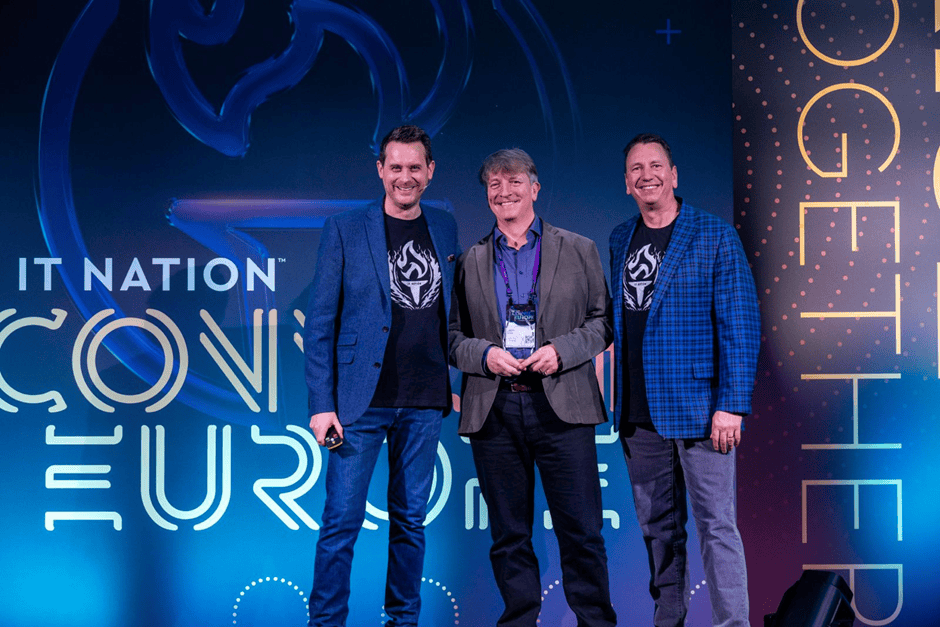
We’re proud to share that our Director, Mark Dale, has officially been awarded the IT Nation, Evolve Partner of the Year 2025 this week, recognising his leadership, Stripe OLT’s commitment to innovation, and the impact the whole team make on the IT community.
AI systems generate plausible answers, not verified truth, meaning misinformation can quickly surface in business workflows. For UK SMEs adopting AI, output validation and governance must now form part of core cyber security controls.
Stripe OLT has achieved the Microsoft Cloud Security Specialisation, proving our expertise in securing Azure and Microsoft cloud environments. Learn what this means for your business.
Stripe OLT is now part of the Microsoft FastTrack Program, giving SMEs direct access to expert-led cloud adoption, security, and digital transformation - at no extra cost. Find out how this accelerates your IT resilience?
Don’t let cyber criminals turn your holiday deals into a data breach. Check out our bite-sized security guide to keep your users, and your business, safe this shopping season.
Across the world, Windows computers have been affected the dreaded Blue Screen of Death (BSOD). This appears to have been caused by an outage of services provided by cyber security provider, CrowdStrike. The issue appears to have impacted a large number of organisations - from banks to airlines. Here are the current advisories.
Stripe OLT has been recognised by Cloudtango as one of the UK's top Managed Service Providers (MSPs) for 2024. Selected from more than 10,000 UK providers, this recognition highlights our commitment to technical excellence, innovation, customer satisfaction and delivering outstanding managed IT services.
This website uses cookies. By using this site you agree to our use of cookies. We use cookies to enhance your experience. To understand the specific cookies we use and how we handle your data, see our Cookie Policy, Privacy Policy and Terms & Conditions. Manage your preferences at any time by clicking the 'View Preferences' button.
Functional
Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes.The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.